Accelerate endpoint investigations with lightweight, non-invasive triage. Deploy Cipher Triage on live suspect machines to harvest volatile memory, running sockets, 30+ forensic artifact categories, and persistent malware indicators with zero forensic contamination.
Test drive the Cipher Triage engine directly in your browser. Configure target profiles, select artifact collection scopes, and witness simultaneous artifact harvesting, P2P detection, and Section 65B evidence container sealing.
When dealing with live threats, full physical disk imaging can result in evidence destruction or hours of unrecoverable downtime. Cipher Triage prioritizes the most volatile and critical forensic artifacts in real-time.
Executes entirely in non-paged memory without modifying source timestamps, overwriting temporary registry hives, or purging volatile memory pools. Read-only handles ensure that uncommitted file caches and memory-injected payloads remain 100% intact for subsequent volatile deep analysis.
Deep packet and process correlation unmasks unauthorized peer-to-peer software (BitTorrent, Tor, I2P, Resilio Sync), encrypted reverse shells, and covert network tunnels disguised as common browser traffic or loopback services. Instantly maps rogue process IDs to outbound IP destinations.
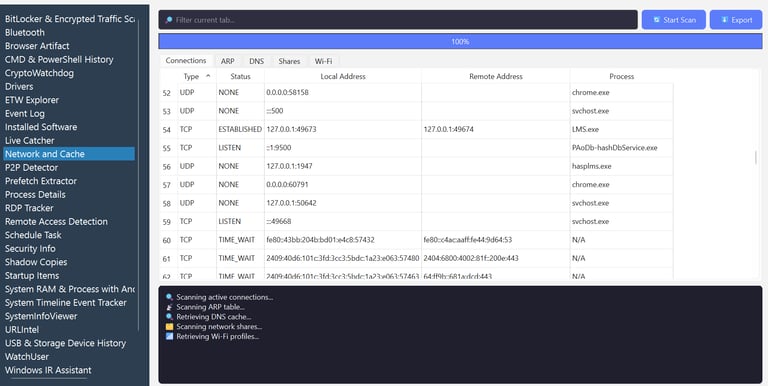
Provides complete situational awareness of the suspect's network footprint: active TCP/UDP socket tables, ARP resolution tables, DNS client cache, open network shares, and historical Wi-Fi connection profiles. Perfect for reconstructing attacker lateral movement across corporate enclaves.
Simultaneously extracts Prefetch (.pf), Amcache.hve, Shimcache (AppCompatCache), UserAssist, BAM/DAM, Shellbags, LNK files, and Volume Shadow Copies (VSS). Integrates them into a unified chronological MACB (Modified, Accessed, Created, Born) timeline ready for courtroom submission.
Cipher Triage harvests evidence across four mission-critical subsystems. Every artifact is parsed into structured JSON and CSV formats with source sector offsets and cryptographic verification.
Explore the intuitive, high-velocity graphical interface of Cipher Triage. Built specifically to deliver instant operational insights to state cyber crime officers, frontline investigators, and enterprise CIRT leads.
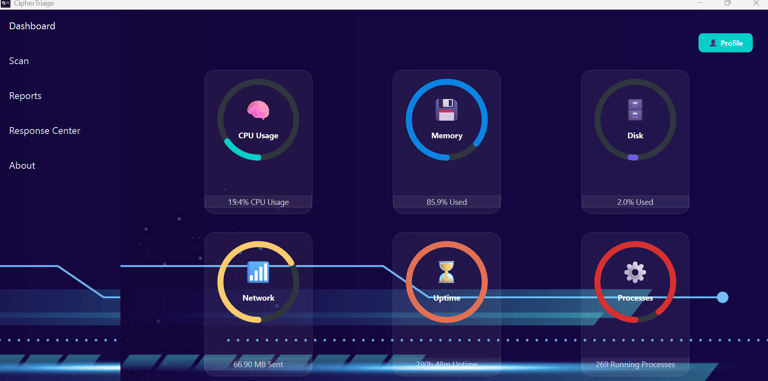
Gain an immediate, high-fidelity snapshot of system health upon USB deployment. Track real-time CPU utilization, physical memory consumption, disk read/write throughput, and active execution threads to instantly identify resource-draining malware or cryptominers.
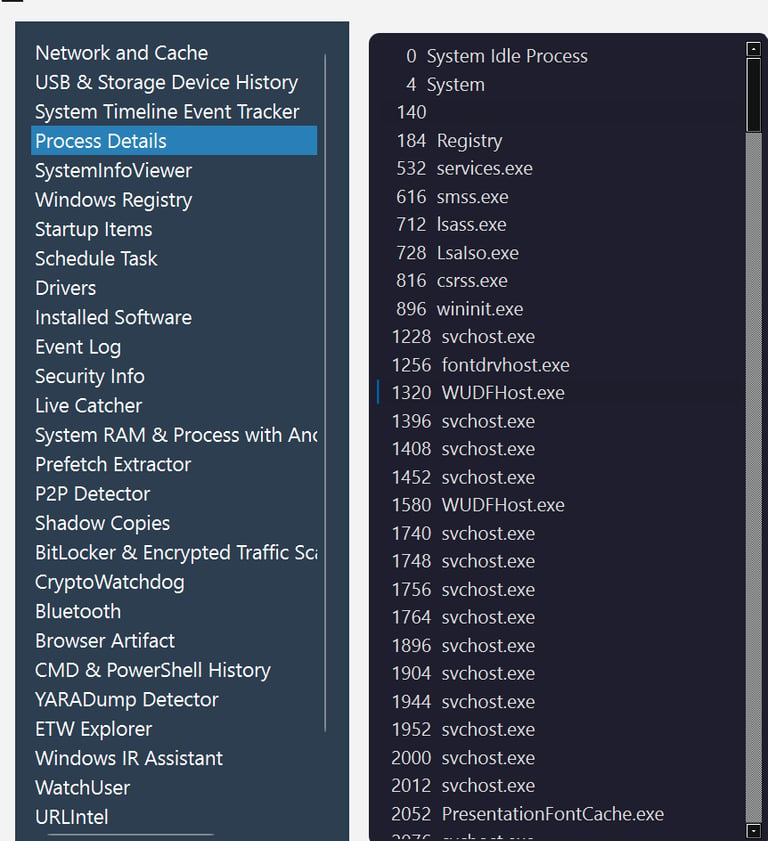
Tailor your triage mission to the exact legal mandate or search warrant parameters. Easily toggle between comprehensive live triage or targeted investigative sweeps — including user profile activities, external storage connections, and deleted file remnants.
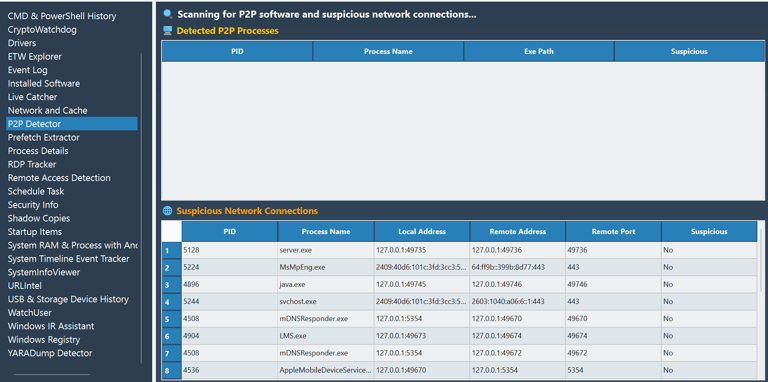
Rogue insiders and advanced threat actors often deploy decentralized peer-to-peer protocols and encrypted proxies to evade enterprise perimeter firewalls. Cipher Triage intercepts suspicious process-level network communications directly at the socket level.
Uncover where the suspect machine has connected and what external infrastructure it communicated with. Correlates active TCP/UDP connections with historical ARP table caches, DNS resolution records, and open network shares.
Compare operational parameters between tactical live triage and traditional bit-stream imaging. Understand when to triage immediately and when to proceed with full drive preservation.
| Operational Dimension | Cipher Triage (Live Endpoint Triage) | Traditional Physical Disk Imaging (E01 / RAW) |
|---|---|---|
| Execution Time | < 3 Minutes (Instant Evidence Output) | 4 to 12+ Hours (Depending on drive capacity) |
| Volatile RAM & Network State | 100% Preserved (Captured live while active) | Permanently lost upon system shutdown or power-off |
| Storage Media Footprint | Compact (1 GB — 8 GB triage archive) | Massive (1 TB — 16 TB dedicated storage per endpoint) |
| On-Scene Actionability | Immediate Go / No-Go Decision for Search Teams | Requires multi-day laboratory processing and ingestion |
| Stealth Threat Detection | Detects in-memory Cobalt Strike, P2P, injected DLLs | Fails to capture fileless, memory-only living-off-the-land attacks |
| Courtroom Admissibility | Section 65B & BSA Sec 63 automated hash certificates | Section 65B physical bit-stream image ledger |
| Operational Deployment | Standalone portable executable via read-only USB | Requires hardware write-blockers and dedicated imaging rigs |
Cipher Triage automatically generates cryptographically signed chain-of-custody certificates compliant with Section 65B of the Indian Evidence Act, Section 63 of the Bharatiya Sakshya Adhiniyam (BSA 2023), and ISO/IEC 27037 standards. Every extracted artifact file is hashed with simultaneous SHA-256 and MD5 checksums, guaranteeing mathematical integrity in judicial proceedings.
Evaluation licenses of Cipher Triage are provisioned exclusively for State Police Cyber Cells, Military CERTs, Intelligence Units, and Certified Enterprise Incident Response teams.